
Universal Fleet Inventory & Telemetry Engine
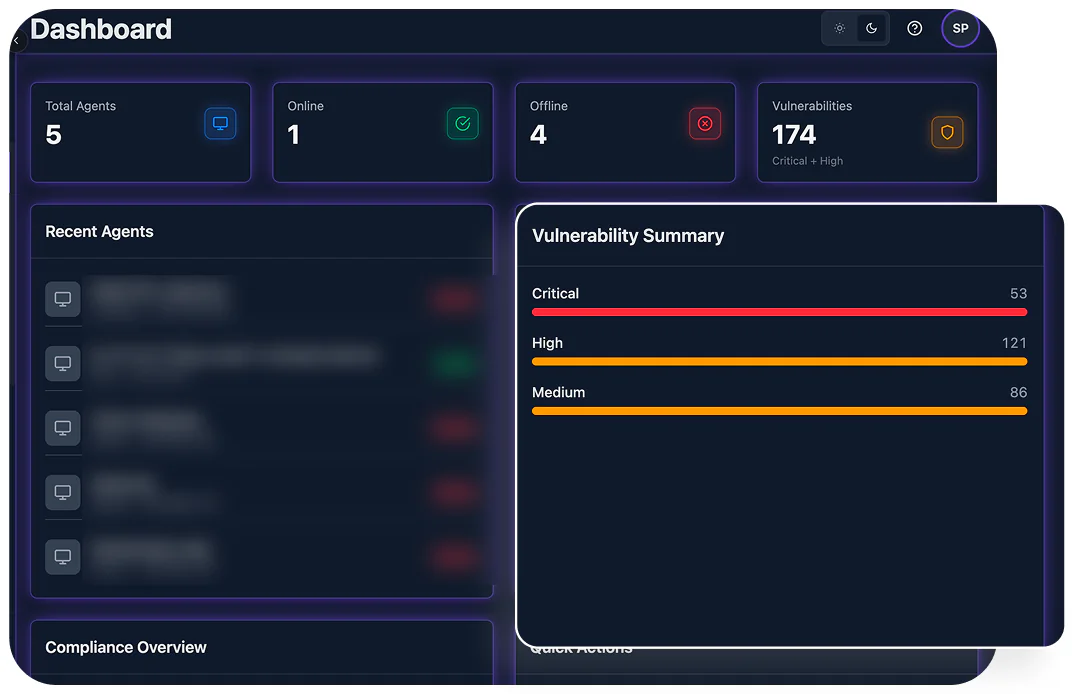
Continuous, deep telemetry ingestion monitoring host health, OS integrity, BitLocker/FileVault encryption state, and application inventories across all corporate endpoints.
Unified Endpoint Management (UEM) & Device Governance
UEM establishes absolute operational visibility and uncompromising control across your entire device ecosystem—laptops, mobile endpoints, cloud servers, and IoT assets. By driving automated OS and third-party patch execution, rigorous configuration auditing, and instant remote policy enforcement into a unified command console, UEM works alongside the d2defence platform and Autonomous AI Engine to proactively eliminate vulnerabilities and lock down every endpoint before adversaries strike.
No credit card required • 10-minute setup • SOC 2 Type II Certified
Total Fleet Visibility Across Windows, macOS, Linux, and Mobile Workloads
Reduction in Exploit Surface via Proactive Automated Patching
Autonomous Host Quarantine and Encryption Enforcement
Elimination of Audit Exposure Across CIS and NIST Compliance Standards
Unmonitored, unpatched, and misconfigured endpoints present an immediate invitation to sophisticated threat actors seeking initial access. Fragmented MDM platforms and legacy management tools leave fatal blind spots across distributed networks. UEM forcefully eliminates device exposure by fusing real-time asset discovery, autonomous patch management, and aggressive compliance enforcement into a unified defense architecture.
Threat Vector / Business Risk
UEM Mitigation Mechanism
Automated real-time asset discovery and continuous agentless/agent-based posture auditing.
Operational Outcome
Absolute operational control over corporate, remote, and unmanaged BYOD endpoints.
Threat Vector / Business Risk
UEM Mitigation Mechanism
Zero-touch automated OS and application patch execution combined with real-time vulnerability scoring.
Operational Outcome
Immediate, proactive closure of known CVEs before exploitation occurs.
Threat Vector / Business Risk
UEM Mitigation Mechanism
Mandatory remote disk encryption (BitLocker/FileVault), instant lock/wipe capabilities, and Autonomous AI Engine autonomous host isolation.
Operational Outcome
Complete prevention of local data exfiltration and immediate containment of lateral adversary movement.
Continuous, deep telemetry ingestion monitoring host health, OS integrity, BitLocker/FileVault encryption state, and application inventories across all corporate endpoints.
Automatically deploys zero-day OS patches and enforces strict CIS benchmark policies across distributed fleets, closing vulnerability windows without operational disruption.
When XDR or TOWER detects adversary activity, Autonomous AI Engine instantly leverages UEM to quarantine compromised hosts, enforce conditional access restrictions, and terminate active adversary sessions in seconds.
Technical deep-dives and platform research from the d2defence security team.
Read Technical ArticlesDeployments across finance, healthcare, energy and the public sector.
Explore All Customer StoriesTier 1: Free Trial
Full UEM feature access for up to 50 endpoints.
Tier 2: Core
Fleet inventory, OS patching, CIS auditing, and baseline policy enforcement.
Tier 3: Growth (Recommended)
Full UEM Suite + Third-Party App Patching + Proactive Autonomous AI Engine Automation.
Tier 4: Enterprise
Complete d2defence Platform + Full Autonomous AI Engine + 24/7 Dedicated SOC Support.
Latest Product News & Updates
Release Notes: UEM v4.5 introduces zero-touch macOS/Windows provisioning and automated BitLocker/FileVault key escrow.
Featured Technical Documentation
Get started with a 14-day free trial or talk to our security architects for a guided demo.