
Autonomous Hacker-Style Pen-Testing Engine
Safely executes automated pen-testing playbooks that simulate MITRE ATT&CK adversary tactics across web applications, microservices, and cloud APIs.
Continuous Automated Pen-Testing & Application Exposure Management
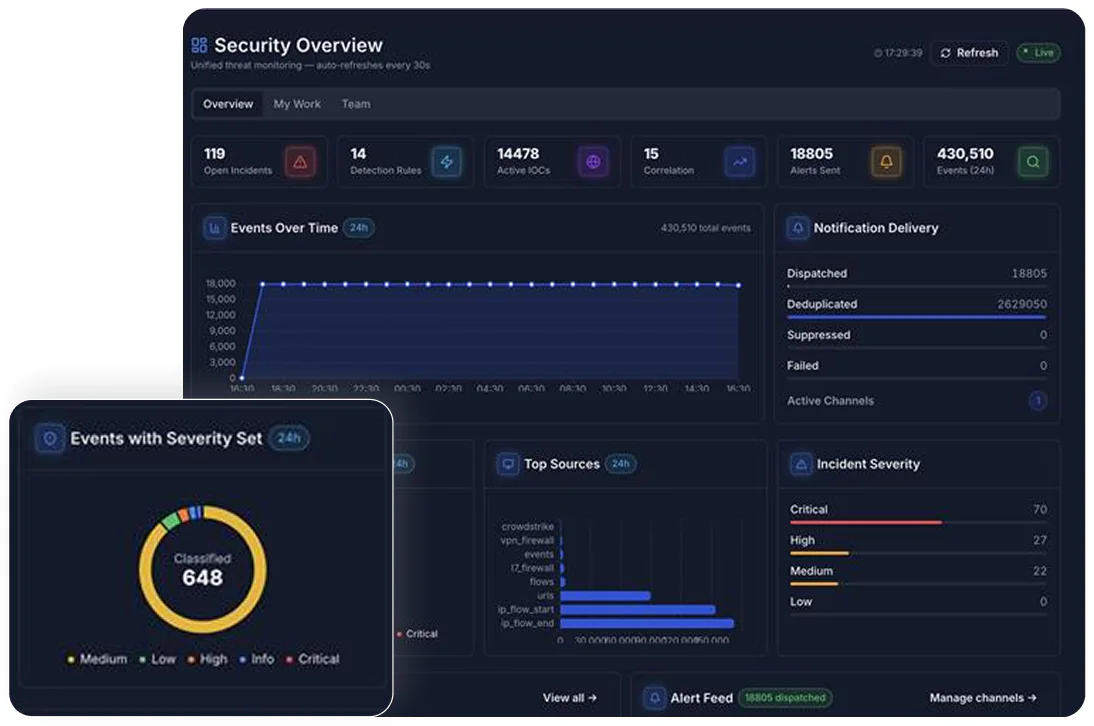
Eradicate adversary footholds before exploitation occurs. detectHub replaces static, annual audits with continuous, autonomous penetration testing and real-time attack surface mapping across web applications, APIs, and cloud infrastructure. By evaluating true exploitability in runtime context, detectHub operationalizes threat intelligence alongside the d2defence platform and Autonomous AI Engine to identify, prioritize, and neutralize attack paths before adversaries strike.
No credit card required • 5-minute setup • SOC 2 Type II Certified
Faster Vulnerability Remediation Cycle
Continuous Autonomous Pen-Testing Coverage (vs. 1x/year manual audits)
Reduction in False-Positive Noise via Contextual Exploit Scoring
Audit Compliance Coverage across OWASP Top 10, NIST, PCI-DSS, & SOC 2
Point-in-time penetration testing leaves applications vulnerable 364 days a year. Rapid CI/CD deployments constantly expose unmapped API endpoints, misconfigurations, and exploitable CVEs. Legacy scanners flood SOC teams with uncontextualized CVSS alerts while adversaries actively map execution paths. detectHub replaces static reports with continuous, adversary-centric penetration testing that contextually prioritizes and tactically neutralizes high-impact threat vectors.
Threat Vector / Business Risk
detectHub Mitigation Mechanism
Continuous automated asset discovery and application attack path mapping across cloud, web, and mobile endpoints.
Operational Outcome
Total attack surface dominance and real-time posture visibility across public and private endpoints.
Threat Vector / Business Risk
detectHub Mitigation Mechanism
Automated hacker-style pen-testing playbooks that safely simulate real-world adversary attack chains in live/staging environments.
Operational Outcome
Validates actual exploitability beyond theoretical CVSS scores, prioritizing true high-risk flaws.
Threat Vector / Business Risk
detectHub Mitigation Mechanism
Native Autonomous AI Engine integration for automated developer ticketing (Jira/GitHub), auto-patch generation, and virtual WAF rule enforcement.
Operational Outcome
Compresses remediation cycles from months to minutes while guaranteeing continuous audit readiness.
Safely executes automated pen-testing playbooks that simulate MITRE ATT&CK adversary tactics across web applications, microservices, and cloud APIs.
Correlates raw vulnerability data with threat intelligence and asset criticality to eliminate false positives and highlight true exposure.
Hands validated vulnerability findings directly to Autonomous AI Engine autonomous agents to execute code fixes, update edge defense rules in SecureEdge, or enforce host quarantine in UEM.
Technical deep-dives and platform research from the d2defence security team.
Read Technical ArticlesDeployments across finance, healthcare, energy and the public sector.
Explore All Customer StoriesTier 1: Free Trial
Full detectHub feature access for up to 50 web apps or API endpoints.
Tier 2: Core
Standard vulnerability scanning, OWASP Top 10 playbooks, and basic reporting.
Tier 3: Growth (Recommended)
Full detectHub Suite + Continuous Automated Pen-Testing + API Threat Surface Mapping + Basic Autonomous AI Engine AI Automation.
Tier 4: Enterprise
Complete d2defence Platform + Full Autonomous AI Engine + Custom Pen-Test Playbooks + 24/7 Dedicated SOC Support.
Latest Product News & Updates
Release Notes: detectHub v4.7 introduces automated GraphQL/REST API pen-testing playbooks and CI/CD GitHub Actions integration.
Featured Technical Documentation
Get started with a 14-day free trial or talk to our security architects for a guided demo.
 SecureEdgeEdge rule
 UEMQuarantine