
Multi-Vector Telemetry Correlation Engine
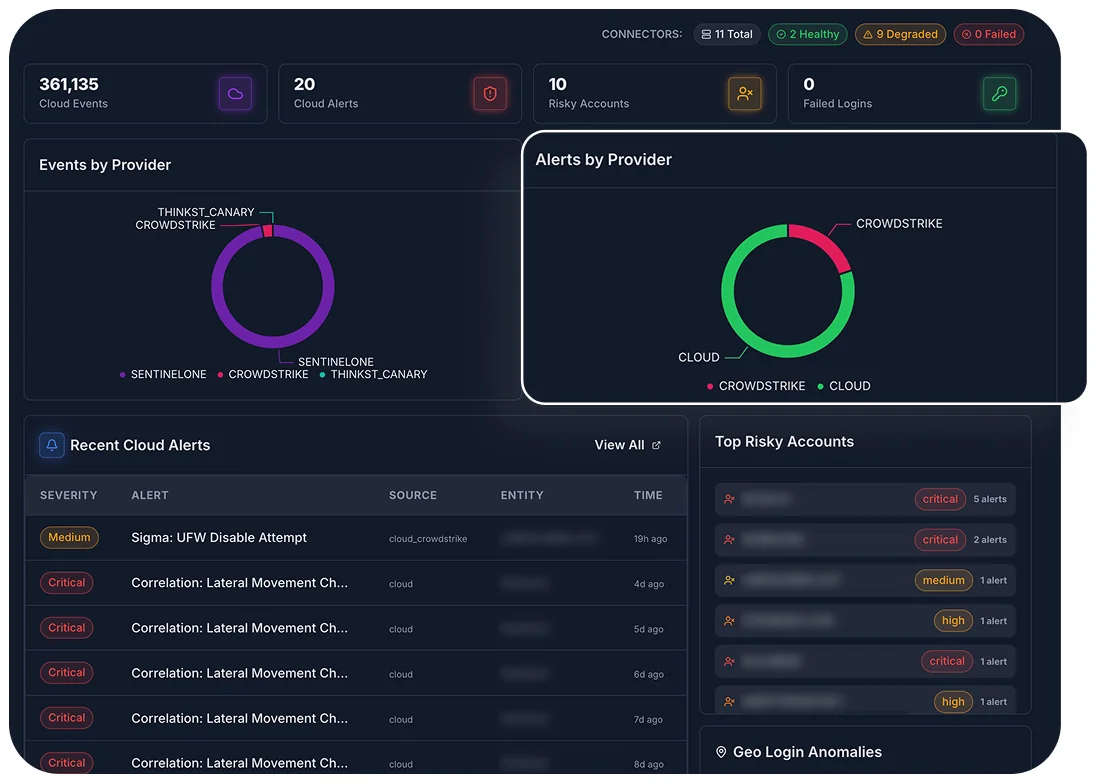
Ingests, normalizes, and correlates cross-domain telemetry in real time to expose hidden threat activity across your hybrid infrastructure.
Autonomous Extended Detection & Response (XDR)
Stop breaches in seconds. XDR unifies telemetry across endpoints, cloud, identity, and networks into a real-time risk graph to eliminate blind spots. Driven by Autonomous AI Engine, XDR detects advanced adversaries, neutralizes lateral movement, and executes automated remediation playbooks before impact occurs.
No credit card required • 5-minute setup • SOC 2 Type II Certified
Adversaries exploit perimeter blind spots across cloud workloads, remote endpoints, and SaaS applications to bypass legacy defenses. Disconnected EDR and SIEM tools overwhelm SOC analysts with alert noise, delaying response when seconds matter. XDR replaces chaos with clarity, transforming telemetry into a continuous risk graph to stop attacks cold.
Faster Response Time (MTTR)
Reduction in Alert Fatigue via Autonomous AI Triage
Threat Neutralization Window
Total Audit Compliance across Major Regulatory Frameworks
01Collect
Threat Vector / Business Risk
XDR Mitigation Mechanism
Continuous agentless and agent-based telemetry ingestion across AWS, Azure, GCP, and hybrid environments into a single control plane.
Operational Outcome
Eliminate attacker hideouts and establish total attack surface dominance.
02Correlate
Threat Vector / Business Risk
XDR Mitigation Mechanism
Real-time threat correlation engine linking network, identity, endpoint, and application signals into a unified risk graph.
Operational Outcome
Expose root causes instantly and eliminate 95% of false positive distractions.
03Respond
Threat Vector / Business Risk
XDR Mitigation Mechanism
Native Autonomous AI Engine integration enforcing automated host isolation, network segmentation, and credential revocation.
Operational Outcome
Neutralize active threats in under 60 seconds with hands-free automated defense.
Ingests, normalizes, and correlates cross-domain telemetry in real time to expose hidden threat activity across your hybrid infrastructure.
Autonomous AI agents execute instant triage, conduct deep forensic analysis, and launch self-healing remediation playbooks without human delay.
Empowers security teams to execute zero-trust containment actions—quarantining hosts or revoking access—instantly with single-click precision.
Technical deep-dives and platform research from the d2defence security team.
Read Technical ArticlesDeployments across finance, healthcare, energy and the public sector.
Explore All Customer StoriesTier 1: Free Trial
Full XDR feature access for up to 50 devices/endpoints.
Tier 2: Core
Core endpoint detection modules, standard logging, and basic threat alerts.
Tier 3: Growth (Recommended)
Full XDR Suite + Multi-Cloud Telemetry + Basic Autonomous AI Engine AI Automation.
Tier 4: Enterprise
Complete d2defence Platform + Full Autonomous AI Engine + 24/7 Dedicated SOC Support.
Latest Product News & Updates
Release Notes: XDR v5.0 introduces automated Kubernetes threat mapping and expanded AWS/Azure cloud connectors.
Featured Technical Documentation
Start your 14-day trial now or schedule a live demo with our threat experts to see autonomous defense in action.